Splunk app by August Schell
IEV Evaluation by August Schell
See what Splunk Integrated Enterprise Value (IEV) for Cisco data is worth in your environment. Measure your eligible Cisco ingest, your effective license consumption at the 0.5x weight, and the Cisco data you are missing, inside your own Splunk.
Splunkbase listing in review. Available now on request.
What IEV means for your license
Under IEV, eligible Cisco data ingested with a supported sourcetype counts at half weight against Splunk ingest licenses. 20 GB/day of eligible Cisco data counts as 10 GB/day. The data itself is unchanged: it is stored, indexed and searched exactly as before.
Your overall license savings equal half of your eligible Cisco share of ingest. Most organizations do not know that share, and eligibility depends on the exact sourcetype, so Cisco data under a custom name or plain syslog does not count. This app measures both.
Four dashboards, one clear answer
Built in Splunk Dashboard Studio, with classic versions included.
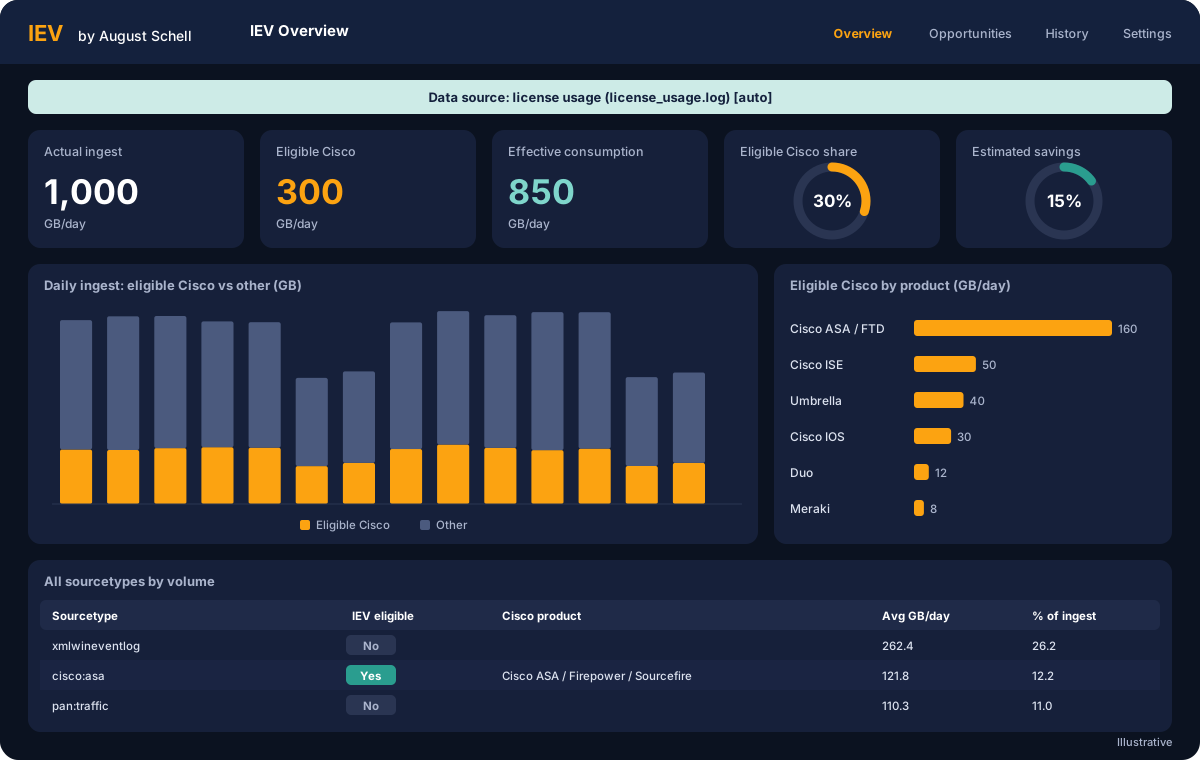
Overview
Actual ingest, eligible Cisco ingest and effective license consumption, with your Cisco share and estimated savings. Breakdowns by Cisco product and by sourcetype show exactly where the value comes from.
Opportunities
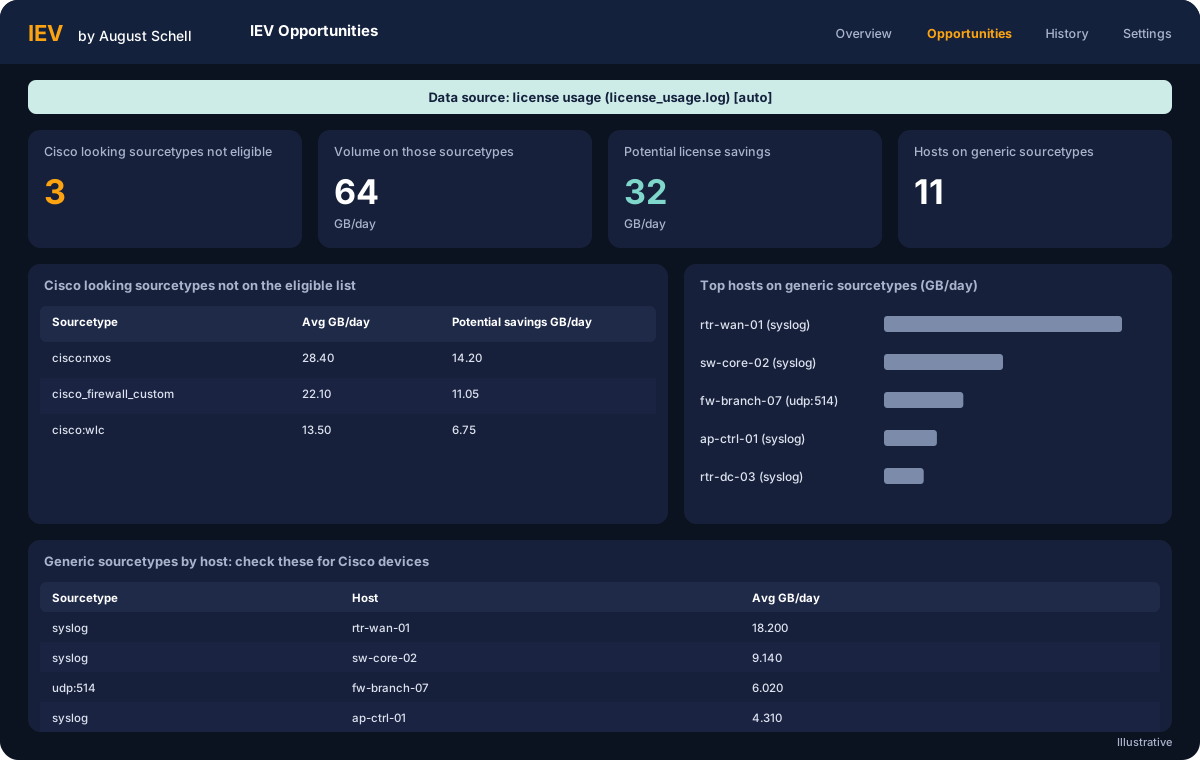
Finds Cisco data that is not landing on an eligible sourcetype, such as custom names or generic syslog, and shows the license savings you could gain by onboarding it correctly. It is a ready made scoping list for cleanup work.
History
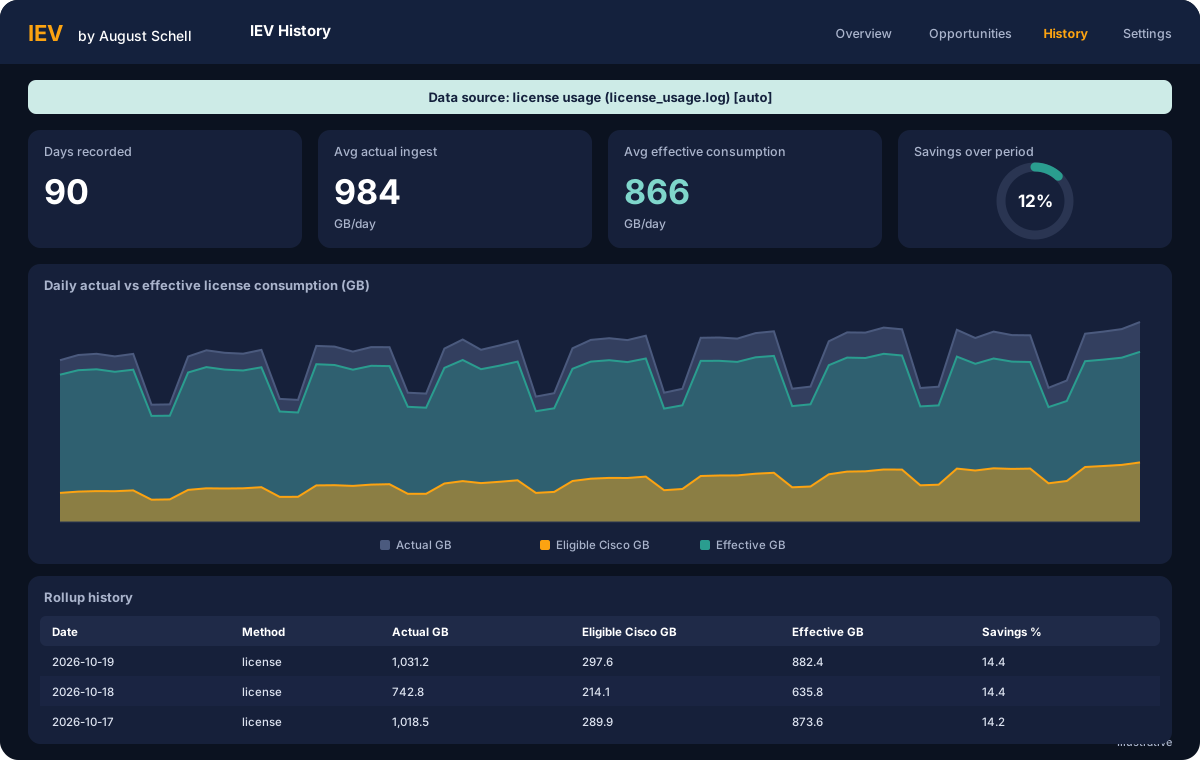
A daily record of actual vs effective consumption, kept beyond the usual 30 day license log retention. Watch the gap grow as more Cisco data is onboarded, and bring real numbers to your renewal.
A fourth Settings page shows the current configuration, the Cisco sourcetypes present and how the app works.
How it measures
License usage
Reads Splunk’s own license usage log by sourcetype. Most accurate, since it matches how Splunk meters.
Event estimate
Event counts multiplied by sampled event sizes. Works when license data is not visible from the search head, with no data models needed.
Demo mode
Built in sample data with a clear banner, so you can walk through the app before pointing it at real data.
Auto mode picks the best available source. Eligibility is matched exactly against the Cisco sourcetypes Splunk publishes for IEV.
Built to run anywhere
- Installs on the search head only. Nothing on indexers or forwarders.
- No Python, custom code, data models or outside connections.
- Works in air gapped, FIPS and Splunk Cloud environments.
- Read only on your data. Settings are admin controlled and survive upgrades.
What you need
- Splunk Enterprise 9.2 or later, or Splunk Cloud Platform.
- An ingest based license. IEV applies to Splunk Enterprise ingest licenses over 100 GB/day and Splunk Cloud Platform ingest licenses, not SVC, vCPU or workload pricing.
- Search access to license usage data for the most accurate results. The estimate covers the rest.
How August Schell helps
- InstallInstall the app on your search head, or we install it for you. No change to data collection.
- ReviewTogether we review your Cisco share, estimated savings and the Cisco data you are missing.
- ActWe move Cisco sources onto supported add-ons and help you bring real numbers to your Splunk renewal.
Request the app
The app is in Splunkbase review and will be publicly available once approved. Until then, request it here and we will send it to you.
You can also ask for an IEV evaluation, where we install the app and review the results with you.
Questions
Which Splunk licenses does IEV apply to?
Splunk Enterprise ingest licenses over 100 GB/day and Splunk Cloud Platform ingest licenses, subject to your order and Splunk’s terms. It does not apply to SVC, vCPU or workload based pricing.
Does the app change my data or my license?
No. It only searches. It reads usage information and stores its own daily history and event size profile in the app. Your data, inputs and license are untouched.
Where do I install it?
On the search tier only: a single instance, the search head (often the Monitoring Console), the search head cluster deployer, or Splunk Cloud Platform.
What if my search head cannot see license usage data?
The app falls back to an estimate based on event counts and sampled event sizes, so it still works. License usage data gives the most accurate numbers.
Is this Splunk’s official IEV calculation?
No. Results are estimates for planning. Splunk validates eligible usage and determines actual IEV treatment under your order and applicable terms.
Results are estimates for planning. Splunk validates eligible usage and determines actual IEV treatment under your order and applicable terms. Splunk and Cisco are trademarks of their respective owners.